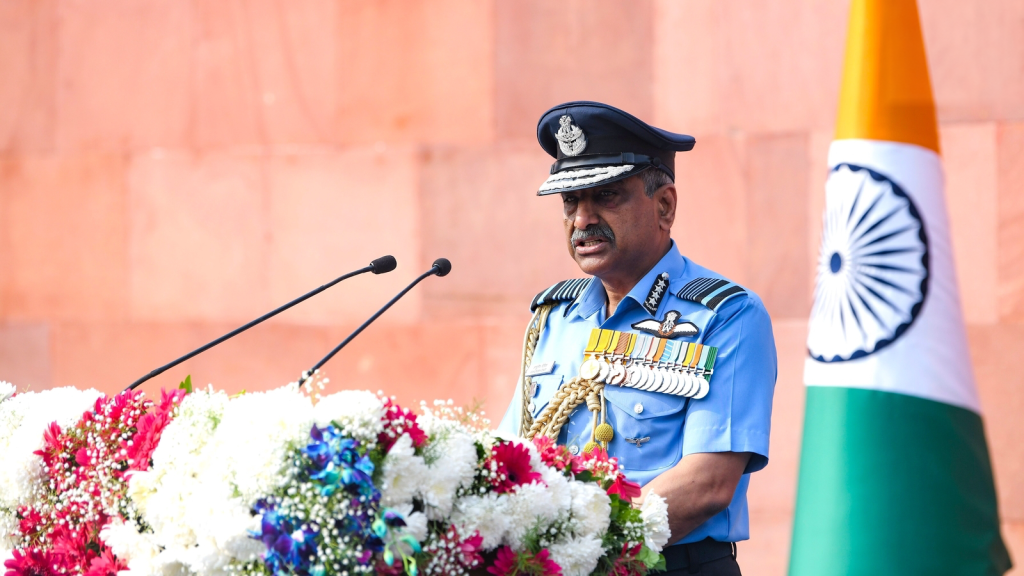
Securing military communication networks from outside intrusion has long relied on physical isolation, yet cutting digital cords does not eliminate vulnerability. Indian Air Force Chief Air Chief Marshal Ashutosh Dixit highlighted this persistent operational challenge in New Delhi, cautioning that while India’s defence networks remain insulated from the wider internet, they are not immune to internal dangers. Dixit pointed out that because national defence networks are air-gapped, adversaries are unable to mount direct internet-based cyber attacks against them, which systematically shifts the vulnerability toward insider threats.
Addressing the ANI National Security Summit 3.0, Dixit noted that the Indian defence establishment is closely tracking cyber espionage and the hazards posed by insiders. To counter these vulnerabilities, a combination of technical mechanisms and institutional protocols has been implemented across defence public sector undertakings, laboratories operated by the Defence Research and Development Organisation (DRDO), and select private sector partners. However, the history of signal intelligence and electronic espionage illustrates that isolating a cable is only the first step in protecting critical data.
The Principle and Limits of Network Air Gapping
An air-gapped system is defined by complete physical isolation: it maintains no physical, wireless, or network link to external infrastructures or the public internet. The architecture is intentionally designed so that data cannot migrate in or out without manual intervention, such as an individual physically transporting storage media like a hard drive, compact disc, or USB flash drive. For an adversary located thousands of miles away, the absence of a network route prevents conventional remote hacking.
Because of this barrier, air-gapping is standard practice across high-stakes environments worldwide. Beyond military command infrastructure and weapons development platforms, air-gapped architectures are used by stock exchanges, biomedical research plants, and insurance repositories to protect mission-critical operations. Israeli cybersecurity researchers who investigate air-gap security have documented that these environments present unique defensive advantages, yet they also create a false sense of absolute invulnerability.
While Dixit did not disclose operational specifics regarding how Indian military systems are segregated, historical precedent demonstrates that physical disconnects have encountered unconventional vulnerabilities since long before the commercial internet existed.
From Bell Labs to SCIFs: The Legacy of TEMPEST
The understanding that sealed electrical devices inadvertently leak information dates back to the Second World War. During that conflict, the United States military relied heavily on electromechanical cipher machines to encrypt sensitive communications into secure codes, which could be decrypted only by recipients possessing the matching operational keys.
In 1943, a researcher at Bell Telephone Laboratories made a critical observation while working near one of these cipher terminals. Whenever the machine clattered to encipher a specific letter, an oscilloscope stationed across the laboratory registered an electrical spike. The instrument was detecting unintended electromagnetic radiation generated by the mechanical switching inside the cipher machine itself. Each minute burst of radio frequency energy corresponded directly to the precise plaintext character being processed. An observer capable of intercepting and deciphering the electromagnetic wave patterns could read raw messages prior to encryption.
Bell engineers conducted a field demonstration to establish the operational significance of the phenomenon. Positioned across the street from an active military cipher center roughly 80 feet away, they captured and reconstructed approximately 75 percent of the scrambled traffic being transmitted within a span of several hours. This demonstration established the reality of compromising emanations.
The United States government subsequently codified counter-surveillance standards under the codename TEMPEST. More than eight decades later, intelligence and military agencies worldwide construct specialized facilities to shield against such acoustic and electromagnetic emissions. Known as Sensitive Compartmented Information Facilities, or SCIFs, these secure rooms feature reinforced doors built to rigorous TEMPEST specifications and acoustically insulated walls designed to prevent speech from carrying into adjacent corridors.
Administrative discipline inside such facilities is equally stringent. Personal cellular devices cannot be brought inside without specific managerial clearance, and commercial smartphones are classified as severe security risks. In tightly restricted areas, personnel must obtain formal administrative authorization merely to transfer files onto an approved optical disc or storage medium.
Crossing the Air Gap: Stuxnet and Physical Vectors
Despite heavy physical controls, external software can breach air-gapped environments whenever physical hardware bridges the divide. The most documented case of this vulnerability occurred in 2010 with the identification of Stuxnet, a sophisticated computer worm engineered to spread autonomously through infected USB flash drives.
Security analysis conducted by Symantec revealed that Stuxnet leveraged previously unknown operating system vulnerabilities to execute automatically upon insertion, without requiring the user to run an executable file. While the worm infected computers internationally, its operational payload targeted specific industrial control systems utilized in manufacturing facilities, pipelines, and uranium enrichment cascades in Iran. Forensic investigators deduced that the malware was initially introduced into an air-gapped facility by an intermediary carrying an infected removable drive, whether intentionally or unwittingly. Later reports published by The New York Times, citing government officials, indicated that Stuxnet was developed jointly by the United States and Israel under a covert program codenamed Olympic Games.
The United States military had experienced a comparable breach two years earlier. In 2008, at an operational base in West Asia, an individual inserted a commercial USB flash drive into a military laptop. The device carried malicious programming placed on it by a foreign intelligence service. William Lynn, who subsequently served as the US Deputy Secretary of Defence, described the incident as the most significant computer breach in American military history.
Once connected, the rogue code uploaded itself directly onto an internal network administered by US Central Command. It moved across classified and unclassified subnets without detection, establishing a conduit to transfer sensitive operational data to external servers controlled by a foreign adversary. The adversary bypassed digital perimeters because an individual physically transported the software across the air gap.
Human Habits and Rogue Hardware
The habit of plugging unfamiliar hardware into computers remains a persistent vulnerability across corporate and military sectors. Sociological and cybersecurity research highlights how easily individuals fall prey to simple physical lures. In a field study conducted by researchers at the University of Illinois Urbana-Champaign, 297 flash drives were placed across a university campus. Approximately 48 percent of those drives were retrieved and connected to computers by individuals, with the first drive plugged in less than six minutes after being dropped. In many instances, the users reported that their motivation was simply an attempt to identify the owner of the misplaced property.
Popular culture has frequently drawn attention to this behavioral flaw. In the television drama Mr. Robot, hackers gain unauthorized access to a correctional facility network by scattering malicious flash drives across an employee parking lot, waiting for an arriving guard to retrieve one and connect it to an administrative terminal. The narrative also depicted physical hardware infiltration, showing an operative bypassing on-site security at a secure data center to conceal a compact Raspberry Pi microcomputer within environmental climate controls.
Unauthorized microcomputers have caused real-world security incidents. In April 2018, an unauthorized Raspberry Pi connected to the network of NASA’s Jet Propulsion Laboratory was exploited by a hacker, according to findings published by NASA’s Office of Inspector General. The attacker remained undetected within the system for approximately 10 months, compromised two of the facility’s three primary networks, and exfiltrated approximately 500 megabytes of data. While the affected JPL network was not completely air-gapped, the breach illustrated how unvetted physical hardware introduces vulnerabilities regardless of network firewalls.
Unconventional Exfiltration Channels
Cybersecurity researchers have demonstrated that once malicious code establishes a presence inside an air-gapped network, it can exfiltrate stolen information through unconventional covert channels that do not rely on traditional data cabling.
Experimental studies have successfully extracted digital data from isolated computers using high-frequency acoustic waves that remain imperceptible to human ears, as well as by capturing subtle variations in radio emissions produced by onboard memory controllers and graphics processing units. In controlled laboratory environments, researchers have transmitted data between adjacent desktop units by modulating internal component temperatures, and have leaked information visually through rhythmic blinking patterns of system indicator LEDs monitored by external cameras.
These specialized exfiltration avenues carry significant operational limitations. Acoustic, thermal, and optical transmission mechanisms yield low transfer rates, often limited to transmitting mere tens of bytes per second—equivalent to a single line of text. More importantly, these side-channel techniques cannot function independently: an attacker must first place functional malware onto the air-gapped host system. Consequently, the operational barrier returns to the physical vector, requiring an individual to introduce the code.
The Core Challenge: Managing the Insider Threat
Because technical perimeters cut off direct internet avenues, adversaries routinely conclude that the most viable method to penetrate an air-gapped network is by manipulating personnel who possess legitimate access credentials. As Dixit emphasized during his address, hostile intelligence services deploy a range of tactics beyond conventional honey-traps to coerce or compromise staff, including financial entanglements, deceptive commercial ventures, and loan operations.
Whether an insider acts with malicious intent, yields to financial pressure, or commits an administrative error by connecting an unchecked USB drive or unapproved peripheral, the human element remains the final variable in maintaining an air gap. For India’s military establishments and defence research ecosystem, defensive readiness requires not only technical segregation of hardware, but also continuous behavioral surveillance and strict institutional controls over everyone who steps past the physical boundary.