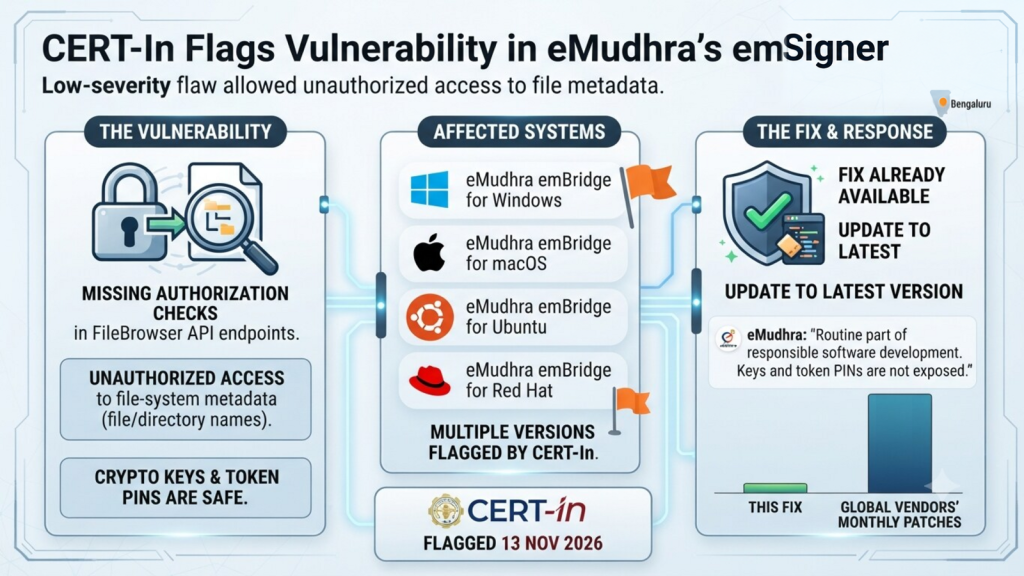
Bengaluru-based digital signature solutions provider eMudhra has released a security update addressing a vulnerability in emBridge, its client-side signing utility used across government portals and enterprise web applications. The patch follows an advisory issued on November 13, 2026, by the Indian Computer Emergency Response Team (CERT-In), which flagged a security weakness that could expose local file-system metadata to unauthenticated actors under specific network conditions.
The emBridge software functions as a bridge that enables web browsers and online services to interact with hardware security tokens and digital signature certificates stored on local user workstations. According to the technical evaluation published by CERT-In, the flaw stems from missing authorization checks within emBridge’s FileBrowser application programming interface (API) endpoints. Because these endpoints execute file system enumeration routines using elevated LocalSystem privileges without adequately verifying the requesting caller’s authorization, an unauthenticated attacker operating on the same local area network (LAN) could trigger unauthorized operations by directing a target to a malicious webpage that communicates with the local HTTPS Web API.
If successfully exploited, the vulnerability allows an attacker to enumerate directory structures and view file and folder names on the host machine. However, CERT-In affirmed that the security defect carries strict operational limitations: it does not permit unauthorized parties to inspect the actual contents of any files, modify or delete stored documents, or execute malicious code on the host device. Crucially, the flaw provides no mechanism to intercept or expose private cryptographic keys or hardware token PINs.
The advisory identified multiple desktop operating systems impacted across specific release tracks:
- eMudhra emBridge for Windows, covering versions 5.9.1.x through 5.9.3.x
- emBridge for macOS (x64), covering versions 3.2.4.x through 3.2.6.x
- emBridge for Ubuntu (x64), spanning versions 3.2.0.x through 3.3.0.x
- emBridge for Red Hat (x64), spanning versions 3.2.0.x through 3.3.0.x
Organizations and individual users relying on these configurations have been advised to install the latest software builds to eliminate exposure.
In response, eMudhra confirmed that a remediation update has been deployed and urged all customers to upgrade immediately, noting that the vulnerability was categorized with a low severity rating. The company emphasized that every digital signature certificate process strictly requires token PIN authentication before any signing operation can occur, ensuring cryptographic integrity remained intact throughout. eMudhra also characterized the patch as routine software maintenance, observing that leading global technology vendors regularly address hundreds or thousands of vulnerabilities in standard update cycles, including recent security rollouts by Microsoft, Oracle, Google, and Adobe.